| Region | Core requirement | Localization mandate? |
|---|---|---|
| European Union / EEA | GDPR-adequate transfer mechanism required for data leaving the bloc | No general mandate, but sector and government-cloud pressure is rising |
| United States | Sectoral and state-level rules (HIPAA, GLBA, CCPA/CPRA and others); CLOUD Act reaches data held by US firms globally | No federal mandate |
| China | PIPL plus Cybersecurity Law; critical information infrastructure operators must store data locally | Yes, for critical infrastructure and important data categories |
| Russia | Federal Law 242-FZ requires personal data on Russian citizens to be first recorded in Russian databases | Yes |
| India | DPDP Act 2023 permits transfers except to government-blacklisted countries | No general mandate, sector-specific rules for payments data |
Why “Data Sovereignty” Means Something Different in Every Region
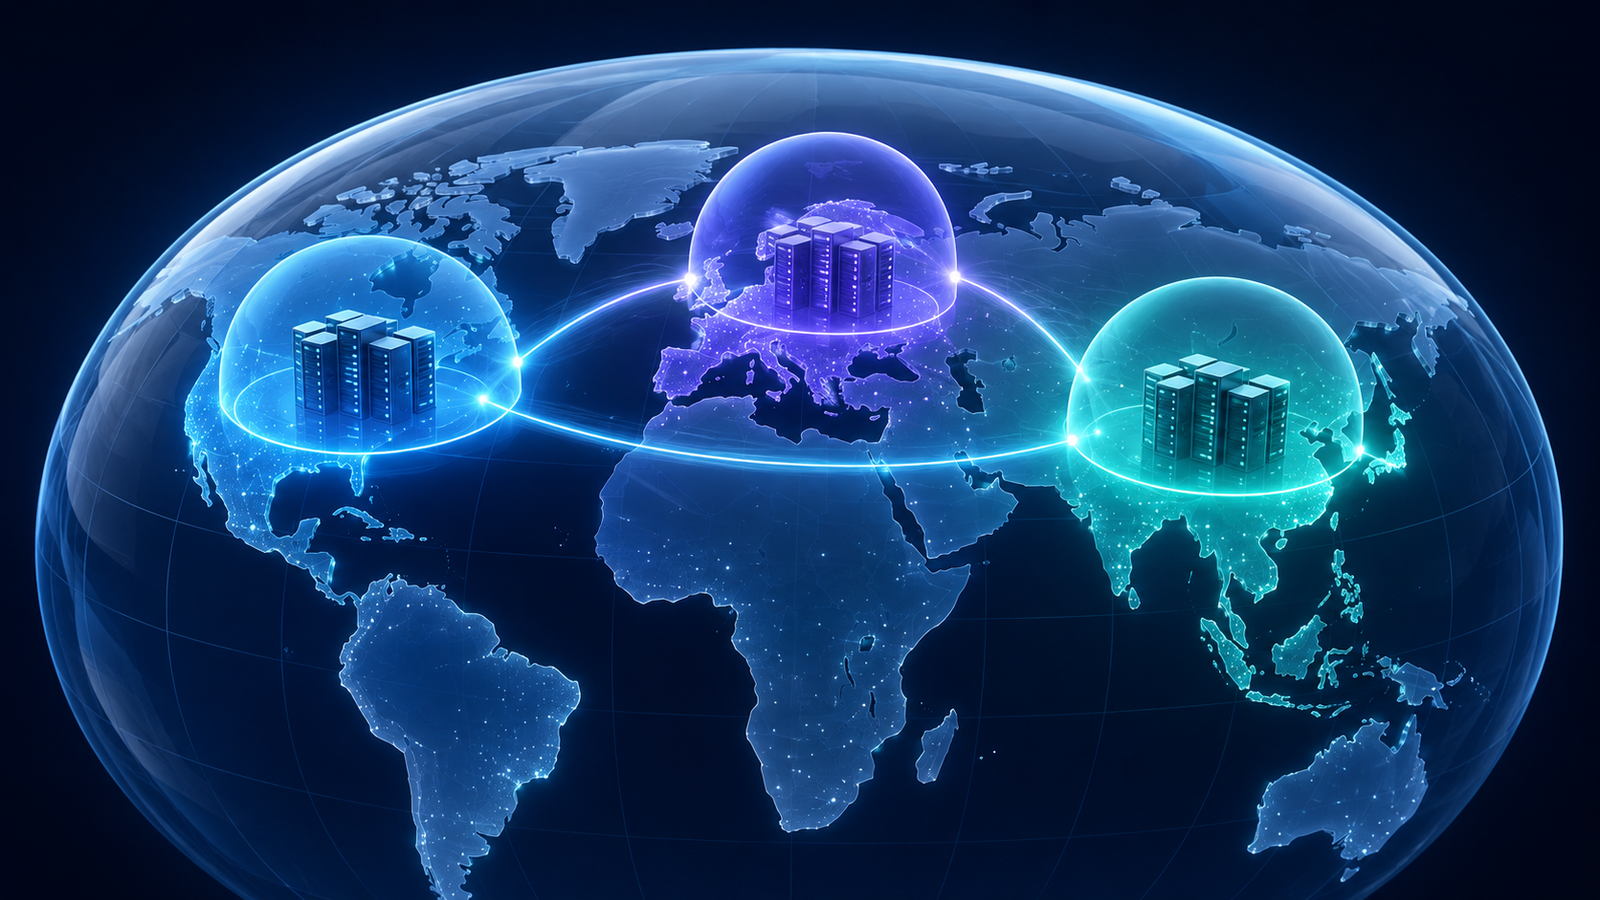
Data sovereignty is one of those phrases that sounds like a single, coherent legal concept until you try to build a compliance program around it. In practice, it bundles together several distinct and sometimes conflicting demands: where data must physically reside, which country’s law governs it regardless of location, who can compel access to it, and whether it can leave a jurisdiction at all. A multinational company operating in the EU, the US, and China is not managing one data sovereignty requirement — it is managing at least three incompatible regulatory philosophies simultaneously, and the gaps between them are where compliance failures happen.
At least 42 countries have now enacted some form of law requiring specific categories of data to be stored within national borders, up from 35 just a few years ago, according to recent tracking of global data localization trends. That number keeps climbing, driven by national security concerns, a desire for domestic technology sector growth, and growing distrust of foreign government access to citizen data. For any organization operating across borders, the practical question is no longer “should we comply with data sovereignty rules” but “which of the dozens of regional variants apply to which of our data flows.”
European Union: Transfer Restrictions, Not Blanket Residency
The EU’s approach is frequently misunderstood as a data localization regime. It is not. The GDPR does not require personal data to stay within the EU or EEA. What it requires is that any transfer of personal data outside the EEA use a recognized legal mechanism — an adequacy decision, Standard Contractual Clauses, Binding Corporate Rules, or a narrower derogation — and that the destination country’s legal environment be assessed for its risk to the data (a Transfer Impact Assessment, a practice cemented by the Schrems II ruling).
That said, the practical effect of EU policy has been to push many organizations toward EU-based processing anyway. Government procurement rules increasingly favor sovereign cloud providers with no foreign parent company. Sector-specific rules — financial services supervisory guidance, health data rules in several member states, and public sector cloud mandates — layer additional residency-like expectations on top of the GDPR’s transfer-mechanism baseline. The EU AI Act, fully applicable from August 2026, adds a further requirement: high-risk AI systems must maintain documented data governance and datasets reflecting the specific characteristics of the deployment environment, which in practice often means keeping training and evaluation data closer to home even without an explicit localization clause.
United States: A Patchwork, Not a Single Regime
The United States has no comprehensive federal data protection law and, as of mid-2026, no federal AI law either. Instead, data sovereignty pressure comes from three directions: state privacy laws (California’s CCPA/CPRA being the most mature, with a growing number of other states following similar templates), sectoral federal laws (HIPAA for health data, GLBA for financial data, FERPA for education records), and the CLOUD Act.
The CLOUD Act is the piece that most confuses non-US organizations. It gives US law enforcement the authority to compel a US-headquartered cloud or communications provider to produce data under its control, regardless of where that data is physically stored. This means a European company using a US hyperscaler’s EU data center does not fully escape US government access exposure purely by choosing an EU region — the legal nexus is the provider’s US incorporation, not the server’s location. This extraterritorial reach is precisely why the EU-US Data Privacy Framework and its ongoing legal challenges, discussed later in this piece, remain such a persistent source of legal uncertainty for transatlantic data flows.
China: The Strictest Localization Regime Among Major Economies
China’s data sovereignty framework is built on three interlocking laws: the Cybersecurity Law, the Data Security Law, and the Personal Information Protection Law (PIPL). Together they impose some of the strictest localization requirements in the world. Critical information infrastructure operators — a broad category covering telecommunications, energy, finance, transportation, and other essential sectors — must store personal information and “important data” within China’s borders. Any cross-border transfer of that data requires a government security assessment before it can proceed.
Even organizations outside the critical infrastructure category face substantial friction: PIPL requires a legal basis for any cross-border transfer, plus one of several mechanisms — a government security assessment, a certification from a recognized body, or standard contractual clauses modeled on (but distinct from) the EU’s SCCs. As of the January 2026 amendments integrating AI governance into the Cybersecurity Law framework, localization obligations now explicitly extend to AI training data processed by critical infrastructure operators, closing a gap that previously left some AI-specific data flows in a gray area.
Three philosophies, one data flow
Picture a single customer record generated by a European user of a US-headquartered SaaS platform with a subsidiary serving Chinese customers. The EU asks: is there a valid transfer mechanism to wherever this record goes? The US asks: is this provider US-headquartered, meaning the CLOUD Act reaches the data no matter where it sits? China asks: does this record contain “important data,” and if so, has it left the country without a government-approved assessment? The same record can be simultaneously compliant under one framework and in violation of another, which is why regional data flow mapping has to happen at the data-element level, not the application level.
Other Jurisdictions Worth Mapping Explicitly
Beyond the three largest regulatory blocs, several other jurisdictions have rules that materially affect global data architecture decisions.
- Russia: Federal Law 242-FZ requires that personal data of Russian citizens be first recorded, stored, and processed using databases physically located in Russia, before any subsequent processing or transfer elsewhere. This is one of the strictest “record locally first” rules among major economies.
- India: The Digital Personal Data Protection Act 2023 takes a comparatively liberal approach, permitting cross-border transfers by default except to countries the government specifically restricts via a blacklist mechanism, a notable contrast to the EU’s allow-list style adequacy approach.
- Brazil: The LGPD closely mirrors GDPR’s structure, permitting transfers through adequacy decisions, standard contractual clauses, and binding corporate rules, without a general localization mandate.
- Australia: The Privacy Act requires reasonable steps to ensure overseas recipients comply with Australian Privacy Principles, with sector-specific residency requirements for certain government and health data.
- Saudi Arabia and UAE: Both have moved toward requiring certain categories of government and critical sector data to remain within national borders, alongside newer comprehensive personal data protection laws modeled partly on GDPR.
| Operational requirement | What it actually means in practice | Regions where it is mandatory |
|---|---|---|
| Data residency | Data must be stored on servers physically located within the country or region | China (critical infrastructure), Russia, parts of Middle East government/health sectors |
| Local processing | Computation on the data must occur within the jurisdiction, not just storage | China (in specific sectors), select government cloud mandates in the EU |
| Government access rules | Defines which government agencies can compel access, and under what legal process | All regions, but scope and speed of compulsion vary enormously (CLOUD Act vs. GDPR-aligned judicial process) |
| Transfer impact assessment | Formal documented risk assessment of the destination country’s legal environment before transfer | EU/EEA (post-Schrems II), increasingly mirrored elsewhere |
| Cross-border approval/notification | Regulator sign-off or notification required before data can leave the country | China (security assessment), Russia (in some cases) |
Common mistake
Treating “data sovereignty compliance” as a single global checklist item is the most common and costly error. A company that stands up an EU region on a US hyperscaler and calls the EU requirement satisfied has solved the wrong problem twice: the GDPR issue was never about server location in the first place, and the CLOUD Act exposure persists regardless of which region the servers sit in. Sovereignty requirements have to be assessed per jurisdiction, per data category, and per legal basis — not per data center.
What worked
Organizations that manage multi-region sovereignty well typically start with a data flow inventory at the data-element level (not the application level), tagging each element with its origin jurisdiction, applicable regulations, and current storage/processing location. From there, they build a decision matrix that flags any element subject to conflicting requirements — for example, a Chinese “important data” classification combined with a US-headquartered processor — and route those specific elements to jurisdiction-appropriate infrastructure rather than trying to solve sovereignty with a single global architecture.
Building a Practical Region-by-Region Compliance Approach
A workable data sovereignty program tends to follow a consistent sequence regardless of which regions are in scope. First, inventory data at the element level and tag its origin jurisdiction — a customer’s billing address alone can trigger different obligations than their support ticket history. Second, map each jurisdiction’s actual requirement type: transfer-mechanism (EU-style), residency-mandate (China/Russia-style), or patchwork-sectoral (US-style), because the compliance action differs completely between these three models. Third, identify where a single infrastructure choice creates conflicting exposure, such as a US-headquartered cloud provider used to serve EU customers, which satisfies no jurisdiction’s concerns simultaneously and needs its own risk acceptance or mitigation (SCCs plus a Transfer Impact Assessment, for instance). Fourth, build a change-monitoring process, because data sovereignty law is one of the fastest-moving areas of global regulation — the January 2026 China Cybersecurity Law amendments and the EDPB’s 2026 Binding Corporate Rules updates are both examples of rules that shifted meaningfully within a single year.
Sovereign cloud offerings — regional cloud infrastructure operated with local ownership, local staff, and contractual commitments to resist foreign government access — have become one of the most common mitigations for the EU and Middle Eastern markets specifically. A deeper look at how these offerings actually work, and where their guarantees fall short, is covered in a dedicated piece on sovereign cloud infrastructure.
- Data residencyA requirement that data physically remain within a jurisdiction’s borders — the strictest and least common form of data sovereignty rule globally.
- Extraterritorial reachA law’s ability to apply to data based on the nationality or headquarters location of the company handling it, rather than the data’s physical location — the defining feature of the US CLOUD Act.
- Critical information infrastructureA regulatory classification, used prominently in China, that triggers the strictest localization and transfer-assessment obligations for operators in essential sectors.
- Transfer impact assessmentA documented evaluation of whether a destination country’s legal environment adequately protects transferred data, required in EU practice since Schrems II and increasingly expected elsewhere.
- Important dataA Chinese regulatory category for data whose loss, leakage, or misuse could affect national security or public interest, subject to stricter cross-border transfer controls than ordinary personal data.
- Government-blacklist transfer modelA regulatory approach, used by India’s DPDP Act, that permits data transfers by default except to specifically restricted destinations — the inverse of the EU’s allow-list adequacy model.
How Regional Rules Interact With Everything Else in a Privacy Program
Data sovereignty decisions rarely stand alone. The transfer mechanism chosen for EU-origin data directly determines what legal paperwork a data flow needs, a topic covered in full in the companion piece on cross-border data transfer mechanisms after Schrems II. Once data is classified by jurisdiction, the anonymization or pseudonymization status of that data can also change which sovereignty rules apply — genuinely anonymized data generally falls outside personal-data-specific residency rules even in strict regimes, a distinction explored in depth in anonymisation versus pseudonymisation. Retention obligations also vary by region in ways that compound sovereignty complexity, since a jurisdiction that mandates local storage may also mandate a different minimum or maximum retention period than the company’s global default, a subject covered in data retention policy design and automated deletion. Organizations building AI systems face an additional layer, since training data sourced from multiple jurisdictions has to satisfy the strictest applicable minimization standard, discussed in data minimisation by design in AI products and, for AI-specific regulatory obligations more broadly, in GDPR and AI compliance.
Where Sovereignty Requirements Are Headed
The trajectory across almost every major region points toward more restriction, not less. The EU continues to tighten transfer scrutiny through EDPB guidance updates, including the 2026 Processor Binding Corporate Rules recommendations. China’s regulatory perimeter keeps expanding to cover new data categories, most recently AI training data under the January 2026 amendments. Even historically permissive jurisdictions like India are expected to issue more detailed sectoral rules as the DPDP Act’s implementing regulations mature. For any organization operating internationally, the realistic planning assumption is that data sovereignty compliance is a continuously maintained program, not a one-time architecture decision.
- Data sovereignty
- The principle that data is subject to the laws of the jurisdiction in which it is collected, stored, or processed, encompassing residency, processing location, and government access rules.
- Data localization
- A specific legal requirement that certain categories of data be stored, and sometimes processed, within a country’s borders.
- Adequacy decision
- A formal determination by the European Commission that a non-EU country provides a level of data protection essentially equivalent to the GDPR, permitting free data transfer without additional safeguards.
- CLOUD Act
- US legislation permitting law enforcement to compel US-headquartered technology companies to produce data under their control regardless of where that data is physically stored.
- Sovereign cloud
- Cloud infrastructure operated under local ownership, staffing, and legal jurisdiction, marketed as reducing exposure to foreign government access and cross-border transfer risk.
Key Takeaways
- Data sovereignty is not one rule set — the EU restricts transfers, China and Russia mandate residency, and the US relies on sectoral and state rules plus the extraterritorial CLOUD Act.
- At least 42 countries now require some category of data to be stored within their borders, up from 35 a few years ago, and the number continues to grow.
- The GDPR does not require EU data residency; it requires a valid transfer mechanism and, since Schrems II, a documented Transfer Impact Assessment.
- The CLOUD Act means a US-headquartered provider’s EU data center does not fully eliminate US government access exposure, since the legal nexus is corporate headquarters, not server location.
- China’s PIPL, Cybersecurity Law, and Data Security Law together create the strictest localization regime among major economies, now extended to AI training data as of January 2026.
- India’s DPDP Act uses a permissive blacklist model, the opposite of the EU’s allow-list adequacy approach, illustrating how differently “compliant transfer” can be defined.
- Effective compliance requires data-element-level mapping, not application-level assumptions, since a single infrastructure choice can satisfy one jurisdiction while violating another.
FAQs
Does the GDPR require personal data to stay physically inside the EU?
No. The GDPR does not mandate data residency. It requires that any transfer of personal data outside the EEA use a valid legal mechanism, such as Standard Contractual Clauses or an adequacy decision, along with a documented Transfer Impact Assessment following the Schrems II ruling.
What makes China’s data sovereignty rules stricter than the EU’s?
China’s PIPL and Cybersecurity Law mandate actual data residency for critical information infrastructure operators and require government security assessments before certain cross-border transfers, whereas the EU’s GDPR focuses on transfer mechanisms and risk assessments rather than mandatory local storage.
Why doesn’t storing data in an EU data center eliminate US CLOUD Act exposure?
The CLOUD Act’s legal reach is based on the corporate headquarters of the provider, not the physical location of the servers. A US-headquartered company can be compelled to produce data it controls even if that data sits in an EU region.
Is there a federal US law equivalent to the GDPR?
No. As of mid-2026, the United States has no comprehensive federal data protection law. Instead, obligations come from sectoral laws like HIPAA and GLBA, a growing set of state privacy laws led by California’s CCPA/CPRA, and the CLOUD Act’s extraterritorial provisions.
How many countries currently have data localization laws?
Tracking as of early 2026 counts at least 42 countries with laws requiring some category of data to be stored within national borders, up from 35 in 2023, reflecting a steady global trend toward stricter localization.
What is a Transfer Impact Assessment and when is it required?
A Transfer Impact Assessment is a documented evaluation of whether a destination country’s legal environment, including government surveillance powers, adequately protects transferred personal data. It became a practical requirement for EU data exporters using Standard Contractual Clauses following the Schrems II ruling.
Does India require data localization under its DPDP Act?
No general localization mandate exists under India’s Digital Personal Data Protection Act 2023. The law permits cross-border transfers by default, restricting them only to specific countries the government blacklists, a more permissive model than the EU’s adequacy approach.
What is “important data” under Chinese law and why does it matter?
Important data is a regulatory classification for data whose loss or misuse could affect national security or public interest. It triggers stricter cross-border transfer controls, including mandatory government security assessments, beyond the baseline requirements for ordinary personal information under PIPL.
References
- Stealthcloud, “The Data Sovereignty Map: Which Countries Require Local Data Storage,” 2026.
- Recording Law, “Data Localization Laws by Country,” 2026.
- Duality Technologies, “Data Sovereignty Laws: A Country-by-Country Guide for 2026.”
- NetApp, “What is Data Sovereignty? Complete Guide for 2026.”
- CookieYes, “Future of Cross-Border Data Transfers: Localisation vs Global Business in 2026.”
- PremAI, “AI Data Residency Requirements by Region: The Complete Enterprise Compliance Guide.”