| Audience | What they actually need from a transparency report | Format that works |
|---|---|---|
| Regulators (for example, under the EU AI Act) | Technical documentation proving conformity, training data summaries, energy usage figures, incident counts | Formal technical documentation package, often per Annex XI and Annex XII templates |
| Downstream deployers integrating the model | Intended use, known limitations, integration requirements, evaluation results | Model or system card published alongside API documentation |
| End users interacting with the system | Clear notice they are talking to an AI, and what the system cannot reliably do | In-product disclosure, plain-language summary |
| The general public and researchers | High-level accountability: what the company is building, what harms it has found, what it is doing about them | Annual or periodic public transparency report |
Transparency Reporting Is Not the Same as Ethics Talk or IP Strategy
Two conversations tend to get tangled together whenever the phrase “AI transparency” comes up, and it is worth separating them before going further. One conversation is philosophical: what does it mean for an algorithm to be fair, who bears moral responsibility for its errors, and how do we balance competing values in system design. The other conversation is about intellectual property: how much of a model’s inner workings can a company disclose before it hands its trade secrets to a competitor.
Both of those conversations matter, but neither one answers the question this guide is actually about: concretely, what does an organization building or deploying an AI system need to write down, publish, or hand to a regulator, and who is the intended reader of each piece. This is an operational question, closer to building a compliance checklist than to debating ethics or defending a patent portfolio. If you already have opinions about algorithmic fairness or trade secret law, you can set them aside for the length of this article. The goal here is a working reporting framework you could actually hand to a compliance team on a Monday morning.
The Regulatory Floor: What Article 53 and Article 50 Actually Require
The single biggest driver of transparency reporting practice right now is the European Union’s AI Act, specifically two articles that are frequently confused with one another. Article 53 applies to providers of general-purpose AI models, meaning the foundation models themselves, and requires them to maintain detailed technical documentation and provide it to downstream providers who integrate the model into their own products. This includes a general description of the model, its intended tasks, its release date and distribution method, and how it interacts with other software or hardware. For models deemed to carry systemic risk, the obligations extend further, including a requirement to publish a sufficiently detailed summary of the content used for training.
Article 50 sits at a different layer, applying to providers and deployers of AI systems more broadly rather than just the underlying models. It covers user-facing transparency obligations: telling people when they are interacting with an AI system rather than a human, labeling AI-generated or manipulated content (including deepfakes) in a machine-readable way, and disclosing when biometric categorization or emotion recognition systems are in use. Both sets of obligations become enforceable from August 2026 in the European Union, with financial penalties that can reach a significant percentage of global annual turnover for serious non-compliance.
The practical distinction matters for anyone building a reporting framework: Article 53 documentation is largely a business-to-business and business-to-regulator artifact, while Article 50 disclosures are consumer-facing and often need to be surfaced directly inside the product interface, not buried in a PDF nobody reads.
| Obligation | Applies to | Core requirement | Primary audience |
|---|---|---|---|
| EU AI Act, Article 53 | Providers of general-purpose AI models | Maintain and share technical documentation, provide information for downstream integration, publish a training data summary for systemic-risk models | Downstream providers and regulators |
| EU AI Act, Article 50 | Providers and deployers of AI systems | Disclose AI interaction, label synthetic and manipulated content, flag biometric or emotion-recognition use | End users and the public |
| Annex XI and XII technical documentation | General-purpose AI model providers | Standardized documentation templates covering architecture, training, and evaluation | Regulators and downstream integrators under non-disclosure terms |
Building the Report: The Five Components That Actually Belong In It
Strip away the legal language and a genuinely useful AI transparency report tends to contain five recurring components, regardless of which jurisdiction is driving the requirement. Skipping any one of them is the most common reason a transparency report reads as compliance theater rather than a real accountability document.
1. A training data summary, not a training data dump
Nobody outside a regulator with a non-disclosure agreement needs, or should receive, a line-by-line list of every document used in training. What a useful public summary provides is category-level detail: rough proportions of web text, licensed content, code, and synthetic data, the approximate time range the data was collected from, and what categories of content were filtered out (personal data, certain categories of copyrighted material, known low-quality sources). The EU AI Act’s own guidance explicitly calls for a “sufficiently detailed summary,” a deliberately flexible standard that avoids forcing disclosure of an exact, competitively sensitive dataset while still giving regulators and researchers something concrete to evaluate.
2. Known limitations, stated plainly
A transparency report that only lists what a model does well is not a transparency report; it is a product brochure. Genuine limitations disclosure names the specific tasks and domains where the model underperforms, known failure modes such as hallucination rates on factual questions, and any populations or use cases the provider explicitly does not support (for example, medical diagnosis or legal advice without human review).
3. Incident counts and post-deployment monitoring
A growing number of providers now publish periodic figures on safety-relevant incidents: how many policy violations were detected, how many jailbreak attempts succeeded before being patched, and how quickly issues were resolved after discovery. This is the transparency reporting equivalent of a security vendor’s breach disclosure practice, and it is often the section regulators scrutinize most closely because it demonstrates whether post-deployment monitoring is actually happening, not just promised.
4. Compute and energy disclosure
This is the newest and least standardized component. As public concern about AI’s electricity and water footprint has grown, a handful of major providers have begun voluntarily publishing figures such as energy consumed per query or per training run. There is currently no common reporting standard across the industry for this figure, which means the numbers different companies publish are not always directly comparable, but the direction of travel is toward more granular disclosure rather than less, particularly as data center electricity demand becomes a visible local political issue in the regions where these facilities are built.
5. A clear escalation and contact path
A transparency report that provides no way for an affected user, a researcher, or a regulator to follow up is missing its most important feature. The best examples include a named contact route for reporting suspected safety incidents, a description of how user feedback is incorporated into the next evaluation cycle, and a commitment to the cadence of future reports (quarterly, annual, or tied to major model releases).
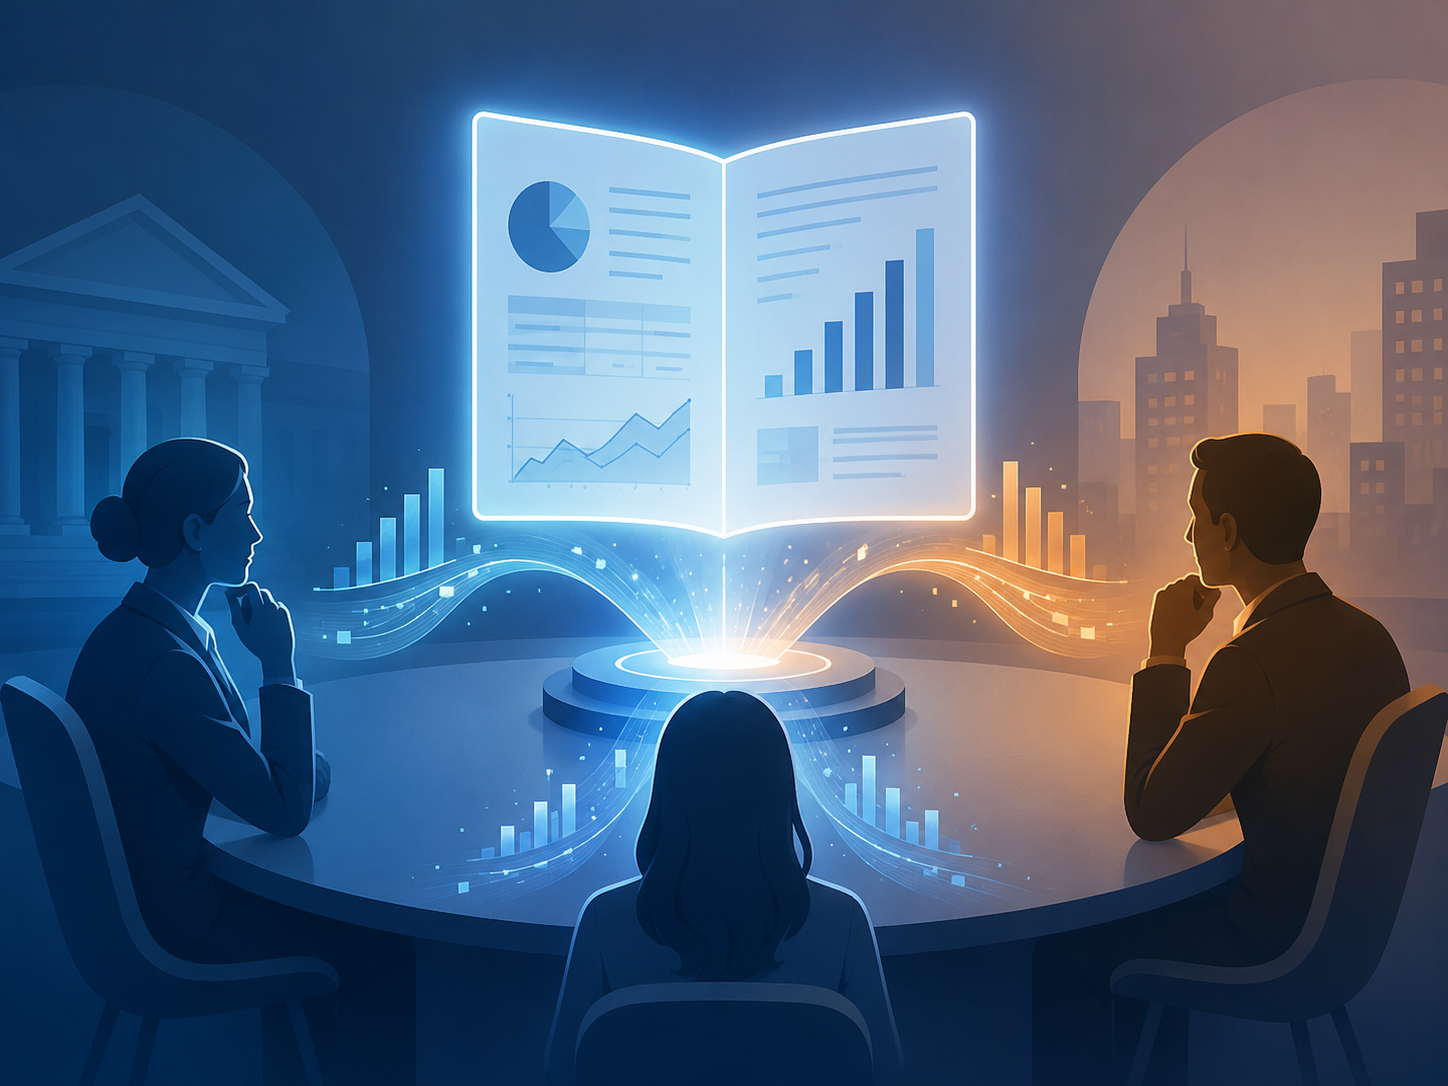
The transparency reporting stack, by audience layer
A layered view showing that the same underlying evidence, training data characteristics, evaluation results, and incident logs, gets repackaged differently for regulators (full technical documentation), downstream deployers (system cards and integration notes), and the public (a readable annual summary).
Common mistake
Publishing one document and assuming it satisfies every audience at once. A regulator-facing technical documentation package written to satisfy Annex XII is usually unreadable to an end user, and a marketing-friendly public summary usually lacks the specificity a downstream deployer needs to build safely on top of the model. Effective transparency reporting programs maintain at least two or three distinct artifacts, calibrated to their actual readers, rather than a single all-purpose document.
What worked
Tiered disclosure with a clear index page. Organizations that publish a single landing page linking out to the technical documentation, the plain-language system card, and the periodic incident summary make it far easier for each audience to self-serve the right level of detail, and it also makes it easier for the organization itself to keep each artifact current without constantly rewriting a single monolithic document.
Beyond the EU: Aligning a Reporting Practice Across Jurisdictions
While the EU AI Act is currently the most prescriptive regime, an organization operating internationally needs a reporting practice that survives contact with more than one regulator. In the United States, there is no single omnibus federal transparency law equivalent to the AI Act, but the NIST AI Risk Management Framework has become the de facto reference point for what “good documentation” looks like, particularly for organizations selling into government contracts, and a growing number of state-level laws require specific disclosures for automated decision systems used in employment or lending. Several US states now require notice when a consumer is interacting with an automated system in a hiring or credit decision, a narrower but functionally similar obligation to the EU’s Article 50 interaction-disclosure requirement.
Elsewhere, transparency obligations often take a different shape entirely. Some jurisdictions require detailed filings directly to a government body rather than public disclosure, meaning the “audience” for that portion of the report is a regulator alone, with no public-facing equivalent. A practical reporting framework accounts for this by separating content into modular blocks, training data summary, limitations, incident log, energy disclosure, each of which can be assembled into a jurisdiction-specific package rather than rewritten from scratch for every regulatory regime you operate under. This modularity is also what makes a reporting practice sustainable as new jurisdictions introduce their own rules over time, since a new regulatory template usually just recombines the same underlying evidence rather than demanding entirely new categories of information.
Who Actually Reads Each Part of the Report
It helps to think of a transparency report less as one document and more as a distribution problem: the same underlying facts, reshaped for different readers with different levels of technical background and different legal standing to demand the information.
Regulators
Regulators need enough technical depth to assess conformity against a specific legal standard, which is why the EU AI Act’s Annex XI and Annex XII templates are so prescriptive: they specify exactly which fields must be completed, in what format, so that assessors across different member states can compare submissions consistently. Regulators also typically receive information under confidentiality protections that do not apply to public releases, meaning the regulator-facing document is often the most detailed of all the versions produced.
Downstream deployers
A company building a customer support tool on top of a foundation model is not trying to assess national-security risk; it needs to know what the model is good at, what it should not be trusted to do unsupervised, and what integration constraints apply (rate limits, data handling commitments, indemnification terms). This audience is generally well served by a system card or model card format, distinct from both the regulator-facing technical file and the public-facing summary.
End users
Individual users rarely read lengthy documentation at all; the relevant disclosure for this audience is usually a short, in-product notice rather than a standalone report. Article 50’s requirement to disclose AI interaction is a good example of a transparency obligation that is satisfied primarily through interface design rather than a published PDF.
The public and researchers
Journalists, academic researchers, and civil society groups typically want the big picture: is the organization improving over time, how does it compare to peers, and what is its track record on the incidents it has disclosed. A periodic public transparency report, published on a predictable schedule, is the artifact that best serves this audience, and it is also the artifact most likely to be cited in press coverage or academic transparency indices that rank providers against one another.
Building Your Own Transparency Reporting Checklist
If you are responsible for standing up a transparency reporting practice inside an organization, the following sequence reflects how mature programs are typically built, starting from the regulatory floor and expanding outward.
- Map your regulatory exposure first. Determine whether you are a provider of a general-purpose AI model, a deployer integrating someone else’s model, or both, since the EU AI Act assigns different obligations to each role.
- Draft the technical documentation package. Use the Annex XI and Annex XII structure as your baseline even if you are not yet legally required to, since it forces disciplined documentation of training data characteristics, evaluation methodology, and known limitations.
- Produce a separate system card for deployers. Translate the technical documentation into a format aimed at engineers integrating your model, focused on practical guardrails rather than legal conformity language.
- Design the in-product disclosure. Work with product design, not just legal, to make sure AI-interaction notices and content labeling are visible at the point of use, not just documented in a policy.
- Commit to a public reporting cadence. Decide whether your public transparency report will be annual, tied to major releases, or quarterly, and publish that cadence publicly so you can be held to it.
- Instrument incident tracking before you need it. Build the internal logging and review process for safety-relevant incidents well before your first public report is due, since retrofitting incident tracking after an incident occurs looks exactly like what it is.
- Systemic risk modelA general-purpose AI model designated under the EU AI Act as carrying heightened risk due to its capability or reach, triggering additional disclosure obligations including a training data summary.
- Sufficiently detailed summaryThe EU AI Act’s deliberately flexible standard for training data disclosure, intended to give regulators and the public real information without forcing release of a full, competitively sensitive dataset.
- System cardA practitioner-facing document describing a model’s intended use, limitations, and evaluation results, distinct from the more legally formal technical documentation package.
- Incident disclosure cadenceThe publicly committed schedule (quarterly, annual, or release-based) on which an organization reports safety-relevant incidents, a key credibility signal separate from the incidents themselves.
- Compute and energy disclosureVoluntary reporting of the electricity or water used to train or run a model, an emerging transparency practice with no common industry standard yet.
Key Takeaways
- A transparency report is not one document; it is a set of artifacts tailored to regulators, downstream deployers, end users, and the public, each with different needs.
- The EU AI Act’s Article 53 governs technical documentation for general-purpose AI model providers, while Article 50 covers user-facing disclosure obligations for AI systems more broadly.
- Both sets of obligations become enforceable from August 2026 in the European Union, with penalties tied to global annual turnover for serious non-compliance.
- A genuinely useful report contains five components: a training data summary, stated limitations, incident counts, compute and energy disclosure, and a clear escalation contact path.
- Training data summaries should use the EU AI Act’s “sufficiently detailed summary” standard, category-level detail rather than an exhaustive content list.
- Compute and energy disclosure remains voluntary and inconsistent across the industry, though a small number of major providers have begun publishing per-query figures.
- Mature transparency reporting programs maintain at least two or three distinct documents rather than one all-purpose report, because a single format cannot serve every audience well.
Glossary
- General-purpose AI model
- Under the EU AI Act, a foundation model capable of performing a wide range of tasks, subject to Article 53 documentation obligations regardless of how it is later deployed.
- Systemic risk designation
- An additional classification applied to the most capable general-purpose AI models, triggering stricter disclosure requirements including a training data summary.
- Technical documentation package
- The formal, regulator-facing set of documents required under EU AI Act Annex XI and Annex XII, covering architecture, training process, and evaluation results.
- Deployer
- Under the EU AI Act, the organization that puts an AI system into use, as distinct from the provider that built the underlying model.
- Machine-readable labeling
- A technical marking embedded in AI-generated or manipulated content that allows automated detection, required under Article 50 for synthetic media.
- Incident count
- A periodic disclosure metric reporting the number of safety-relevant events, such as policy violations or successful jailbreaks, detected in a given reporting period.
FAQs
What is the difference between EU AI Act Article 53 and Article 50?
Article 53 applies to providers of general-purpose AI models and requires technical documentation and, for higher-risk models, a training data summary shared with downstream integrators and regulators. Article 50 applies more broadly to providers and deployers of AI systems and covers user-facing disclosures, such as informing people they are interacting with an AI or labeling synthetic content.
Do I need to publish my exact training dataset?
No. The EU AI Act requires a “sufficiently detailed summary” of training content for higher-risk general-purpose AI models, not an exhaustive itemized list. This standard is intentionally flexible, aiming to give regulators and the public meaningful category-level information without forcing disclosure of a full, competitively sensitive dataset.
Who is the actual audience for a transparency report?
There is no single audience. Regulators need conformity evidence and full technical detail, downstream deployers need practical integration and limitation information, end users need a brief in-product disclosure, and the public and researchers need a periodic, readable summary of overall practices and incidents.
What counts as a safety-relevant incident worth disclosing?
Common categories include confirmed policy violations by the model, successful jailbreak or prompt-injection attempts that bypassed safeguards, factual errors serious enough to cause real-world harm, and any unauthorized data exposure. Mature reporting programs define these categories in advance so counting is consistent from one reporting period to the next.
Is disclosing energy and compute usage legally required?
Not yet, in most jurisdictions. As of now, no common regulatory standard mandates energy or compute disclosure, which is why the figures published by different providers are not always directly comparable. A small number of major providers have begun voluntarily publishing per-query energy figures in response to public and investor pressure.
What is a system card and how is it different from a technical documentation package?
A system card is a practitioner-facing summary describing a model’s intended use, known limitations, and evaluation results, written for engineers and product teams integrating the model. A technical documentation package is the more formal, legally structured artifact required by regulators, typically containing more granular detail and submitted under confidentiality protections.
How often should a transparency report be published?
There is no single required cadence outside specific regulatory deadlines, but mature programs commit publicly to a schedule, commonly annual or tied to major model releases, and stick to it. The consistency of the cadence itself is a credibility signal independent of the content in any single report.
What penalties apply for non-compliance with EU AI Act transparency obligations?
Non-compliance with the Article 50 transparency obligations can result in fines of up to fifteen million euros or three percent of total worldwide annual turnover for the preceding financial year, whichever amount is higher, for offending organizations.
References
- Sidley, “EU AI Act Transparency Obligations: Preparing for Compliance by 2 August 2026”
- artificialintelligenceact.eu, “The EU AI Act’s Transparency Rules: A Practical Guide to Article 50”
- artificialintelligenceact.eu, “Annex XII: Transparency Information Referred to in Article 53”
- William Fry, “Part 1: AI Act Articles 50(1) and 50(2) Transparency Obligations”
- European Commission, Digital Strategy consultation on draft transparency guidelines under the AI Act
- Stanford HAI, “Transparency in AI is on the Decline,” Foundation Model Transparency Index coverage
- Axios, “AI boom puts Big Tech’s transparency to the test”
- Sify, “The Growing Push for Transparency in AI Energy Consumption”
For related reading on this site, see our companion pieces on the broader ethics of AI transparency, accountability, and fairness, balancing AI disclosure against trade secret protection, auditing agentic AI decisions no human reviewed, a practical EU AI Act compliance walkthrough, what belongs in a model card or system card, and building an AI incident response process.