| Approach | What Gets Checked | When It Runs | Who Makes the Final Call |
|---|---|---|---|
| Traditional manual compliance review | Documents, screenshots, self-reported attestations | Quarterly or annual audit cycles | Compliance officer or auditor |
| Policy as code (automated) | Machine-readable conditions checked against live system state | Every commit, deployment, or inference call | Policy engine for defined rules; humans for exceptions |
What Policy as Code Actually Means for AI Governance
Policy as code is the practice of writing governance, security, and compliance rules as machine-readable files that a software engine can evaluate automatically, rather than leaving those rules trapped in PDF policy documents that only humans read. The idea did not start with artificial intelligence. It grew out of cloud infrastructure and security engineering, where teams got tired of finding out about a misconfigured server two weeks after it shipped, during an audit, instead of the moment it was created. Tools such as Open Policy Agent popularized the pattern by giving engineers a declarative language, Rego, for expressing rules like “no storage bucket may be publicly readable” or “no deployment may skip a security scan,” and a lightweight engine that could answer those questions in milliseconds.
Applying the same idea to AI governance is a natural extension, and it is happening quickly in 2026. Instead of a compliance team manually confirming, once a quarter, that a model card was filled out or that a bias audit happened before a hiring tool went live, a policy-as-code system checks for that evidence continuously, as part of the same pipeline that ships the model or serves the request. Industry compliance research frames this shift well: compliance can no longer be treated as a periodic audit exercise or a final checkpoint before release, because AI systems change too often and too fast for point-in-time reviews to keep up.
The appeal is straightforward. A policy engine does not get tired, does not forget to check the twelfth item on a list, and produces the same answer given the same inputs every time. For AI systems specifically, that consistency matters because the underlying models, prompts, and datasets change constantly, and a rule that was satisfied last month may silently stop being satisfied after a routine fine-tune or a new data source gets connected upstream.
How a Policy Engine Fits Into an AI Pipeline
Most implementations put policy-as-code checks at one or more of three points: before code or a model ships, while a system runs, or at the moment a specific inference request is served. Each point catches a different category of problem, and mature governance programs typically use more than one.
| Enforcement Point | What It Typically Catches | Latency Tolerance | Common Tooling Pattern |
|---|---|---|---|
| CI/CD pipeline gate | Missing documentation, unapproved data sources, absent bias-audit record | Seconds to minutes acceptable | Policy engine invoked as a pipeline step before merge or deploy |
| Runtime or sidecar monitoring | Configuration drift, unauthorized model version in production | Near real time | Sidecar or service mesh calling out to a policy decision point |
| Inference-time guardrail | Disallowed output categories, missing required disclosure, blocked input types | Milliseconds, on the request path | Policy engine embedded in or adjacent to the model-serving layer |
Rego and the Declarative Model
Open Policy Agent, the most widely referenced engine in this space, expresses rules in a language called Rego. Rather than writing imperative code that says “loop through every field and check it,” Rego lets an author declare what a valid state looks like, and the engine figures out how to evaluate that declaration against whatever input it is given. This matters for AI governance because the same declarative rule can be reused across many different systems: a rule requiring that a bias audit dated within the last twelve months must exist for any tool used in a hiring decision does not need to know anything about the specific hiring tool, only about the shape of the audit record it expects to see.
Open Policy Agent itself, created by Tim Hinrichs, Torin Sandall, and Teemu Koponen, graduated from the Cloud Native Computing Foundation in February 2021 as the foundation’s first project focused entirely on authorization. That lineage in cloud infrastructure security is exactly why the pattern transfers so cleanly to AI governance: both problems boil down to deciding, quickly and consistently, whether an action is allowed given the current state of the world.
Where Inference-Time Checks Change the Equation
Pipeline gates catch problems before a model ships. Inference-time guardrails are different in kind, because they evaluate a live request, with live context, and decide in real time whether to allow, block, or modify a response. For an AI governance program, this is the enforcement point that lets a company say, credibly, that a rule is not just documented but actually operative every time the system is used. One analysis of this pattern describes agents sending request context, such as identity, target dataset, and intended query, to a policy engine over HTTP, receiving a decision back, and blocking the action if the policy engine denies it. That loop, repeated millions of times a day, is what automated compliance concretely looks like in production rather than in a slide deck.
Translating Regulatory Text Into Executable Rules
The hardest part of policy as code is rarely the engine. It is the translation step: turning a paragraph of legal or regulatory prose into a condition a machine can evaluate as true or false. Regulatory language is written for human interpretation and deliberately leaves room for judgment, context, and precedent. Executable rules need something much narrower: a specific field, a specific threshold, a specific presence-or-absence check.
Recent academic work has started treating this translation problem as a research question in its own right rather than an implementation detail. A 2026 paper on executable governance for AI examines how large language models can help translate written policies into formal rules, while flagging that the translation itself introduces a new source of error that governance teams have to audit. A related project, ArGen, applies policy-as-code style auto-regulation directly to generative AI outputs using reinforcement learning techniques, effectively trying to make the model itself internalize the executable rule rather than checking it only at the boundary. Both lines of work point to the same conclusion: the translation from policy text to executable rule is not a one-time engineering task, it is an ongoing discipline that needs its own review process.
In practice, most teams handle the translation manually today, with a compliance or legal reviewer working alongside an engineer to decide exactly what a rule should check. A workable pattern looks like this: identify the specific, checkable fact the regulation is actually asking for, write the rule to check for that fact and nothing more, and explicitly document what the rule does not cover so nobody later assumes a passing check means full compliance with the underlying regulation.
| Regulatory Requirement (Plain Language) | What an Executable Rule Can Check | What It Cannot Check |
|---|---|---|
| Conduct a bias audit before deploying a hiring tool | An audit record exists, is dated within the required window, and references the correct tool version | Whether the audit methodology was actually rigorous or independent |
| Provide a meaningful explanation for automated decisions | An explanation field is populated and non-empty for every logged decision | Whether the explanation is actually intelligible or accurate to the affected person |
| Maintain human oversight of high-risk AI systems | A named reviewer field and a review timestamp exist on flagged cases | Whether the human reviewer engaged critically or rubber-stamped the output |
What Automated Compliance Checks Can Verify
It helps to be precise about what a policy engine is actually good at, because overselling this capability is one of the most common failure modes in early AI governance programs. A well-built rule set can reliably confirm:
- That a required document, record, or field exists and is not empty.
- That a timestamp falls within an acceptable window, such as an audit completed in the last twelve months.
- That a specific version of a model, dataset, or prompt matches an approved allow-list.
- That an output does not contain a disallowed category of content, based on a classifier or pattern match.
- That a workflow step was not skipped, because the system that would trigger the next step never received the required signal.
Every one of those is a presence-or-absence, threshold, or pattern-match question. None of them require the engine to understand whether the underlying substance was good. That distinction is the entire argument for why automated compliance supplements human judgment rather than replacing it.
The Limits of Automation: Where Human Judgment Still Rules
The Institute for Law and AI has written specifically about automated compliance and the regulation of AI, and one of the more useful framings from that line of work is the distinction between checking for the presence of a control and evaluating the substance of a control. A policy-as-code rule can confirm a bias audit happened. It cannot confirm the audit was competent, that the statistical test chosen was the right one for the underlying data, or that an edge case that falls outside the audit’s assumptions was actually caught. Genuinely ambiguous cases, the ones where reasonable, well-informed people disagree about the right outcome, are exactly the cases automation is worst at handling, because they are the cases that resist being reduced to a checkable condition in the first place.
This is not an argument against automating compliance. It is an argument for being honest about where the boundary sits. A useful rule of thumb: if a compliance question can be answered by looking at one field in one record, it is a good candidate for a policy-as-code rule. If answering it requires weighing competing values, considering context that is not captured anywhere in the system, or making a judgment call about intent, it needs a human in the loop, and the policy engine’s job is only to make sure that human review actually happens rather than getting skipped.
Common mistake
Teams sometimes treat a green checkmark from the policy engine as proof the underlying regulatory requirement was satisfied, when it only proves the specific, narrow condition that was coded was met. A passing automated check on whether a bias audit record exists says nothing about whether that audit was methodologically sound. Governance teams need a separate, periodic process to spot-check the substance behind the automated signal, not just the signal itself.
Continuous Assurance Versus Periodic Audits
Industry analysts have described this shift as moving from compliance to continuous assurance, and the framing is a useful way to compare what changes operationally when a team adopts policy as code instead of relying purely on scheduled audits.
| Dimension | Periodic Audit Model | Continuous Assurance Model |
|---|---|---|
| Detection lag for a new violation | Up to one audit cycle, often months | Minutes to hours |
| Evidence trail | Manually assembled for the audit window | Generated automatically as a byproduct of every run |
| Coverage | Sample-based, often a subset of systems | Every deployment or request that passes through the gate |
| Cost profile | Concentrated spikes around audit season | Spread out, with upfront engineering investment |
The business case is not purely theoretical. Industry compliance research puts the average total cost of non-compliance in regulated environments at roughly 14.82 million US dollars, compared with roughly 5.47 million US dollars for organizations that stay compliant. That gap is a big part of why continuous, automated assurance has moved from a nice-to-have to a budget line item at companies deploying AI in regulated contexts.
Building a Policy-as-Code Pipeline for AI Governance
Teams starting from zero tend to get better results by sequencing the work rather than trying to encode every policy at once.
- Inventory the AI systems in use and classify each one by regulatory exposure, so effort goes first toward the systems with the highest risk of causing real harm or triggering an enforcement action.
- Pick a small number of high-value, low-ambiguity rules to encode first, such as confirming a model card exists for every production model or that no model deploys without a logged risk classification.
- Choose an enforcement point for each rule based on how quickly a violation needs to be caught: pipeline gates for anything that can wait for the next deployment, inference-time checks for anything that needs to block a live request.
- Write the rule narrowly, document explicitly what it does and does not verify, and store that documentation next to the rule itself so it does not drift out of sync.
- Route every automated denial to a visible queue that a human reviews, rather than silently blocking and moving on, so genuinely ambiguous or borderline cases surface to a person instead of disappearing into a log file.
- Revisit the rule set on a fixed schedule, because regulations change, models change, and a rule that made sense a year ago may now be checking the wrong thing entirely.
What worked
Organizations that started with three to five narrow, well-documented rules and expanded gradually reported far fewer false positives than teams that tried to encode an entire regulatory framework in one pass. Narrow rules with clear boundaries also made it much easier to explain to auditors exactly what the automated system was and was not verifying, which auditors consistently responded well to.
Frequently Overlooked Considerations
- Rule driftA rule written against last year’s regulatory text can silently become wrong when the regulation is amended, with no error thrown because the rule still executes successfully.
- False confidencePassing automated checks can create a false sense that full compliance was achieved, when only the narrow, codified slice of the requirement was actually verified.
- Ownership gapsRules written by engineers without ongoing legal review tend to drift away from what the regulation actually requires over time.
- Exception handlingSystems that only support allow or deny, with no path for a documented, reviewed exception, push teams to either over-block legitimate work or quietly disable the rule.
- Auditability of the rules themselvesRegulators and auditors increasingly want to see the rule logic itself, not just its output, which means rule code needs the same version control and review discipline as production software.
- Cross-jurisdiction conflictsA single AI system operating across regions may need different rule sets active simultaneously, and reconciling conflicting requirements is a design decision, not something the engine resolves on its own.
- Translation review cadenceBecause turning legal text into code is itself error-prone, mature programs schedule a recurring review specifically of the translation step, separate from reviewing the rules’ technical correctness.
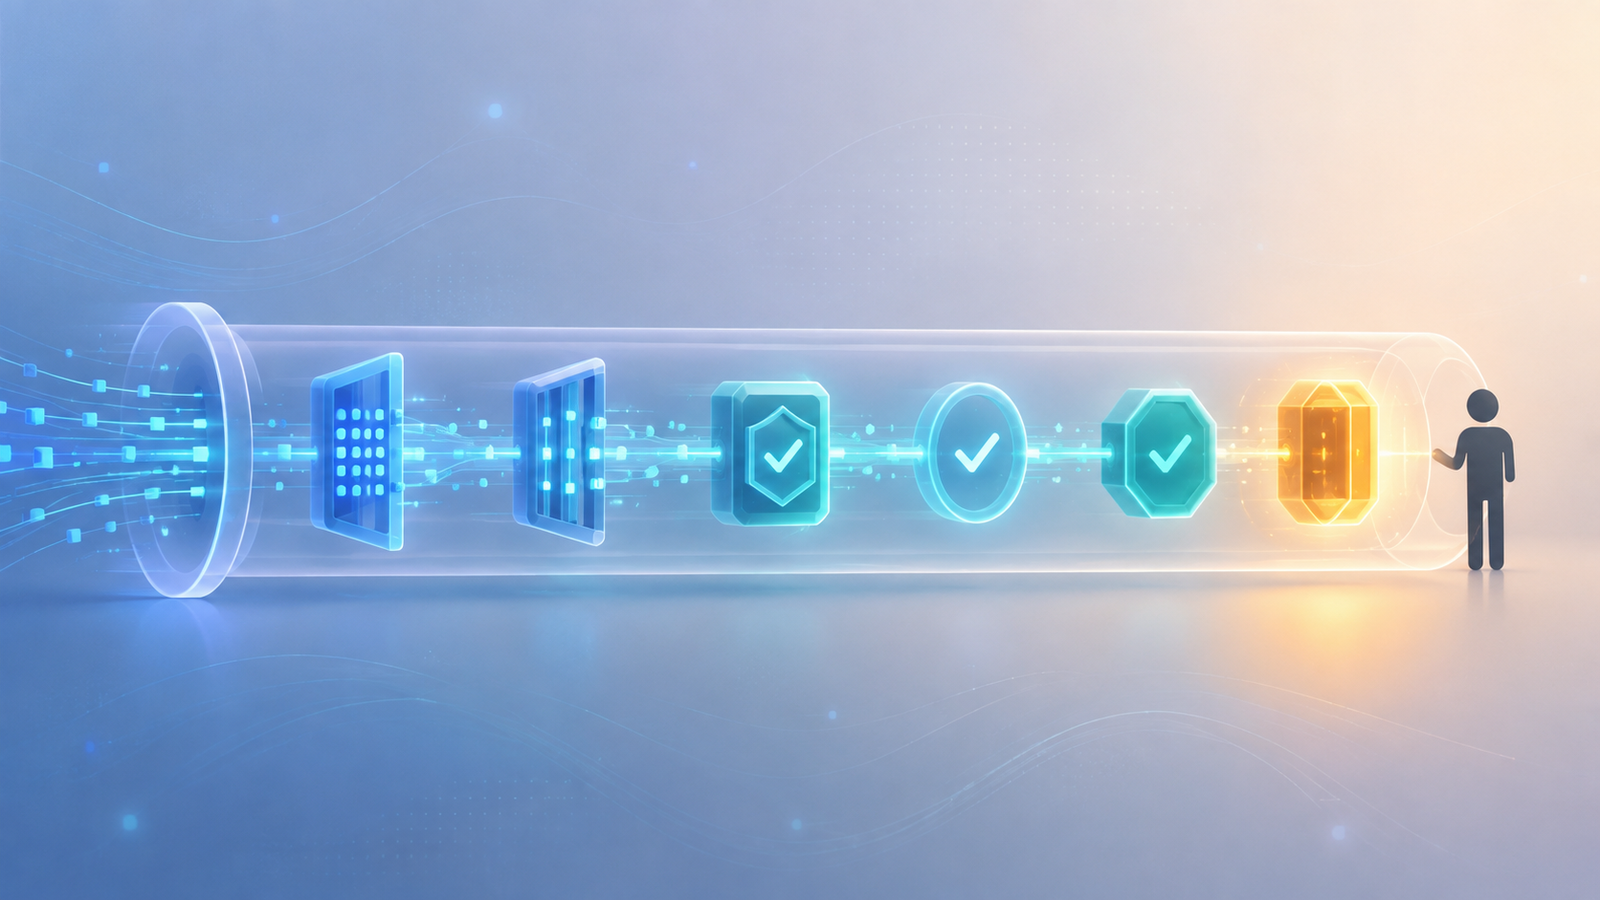
A three-gate compliance pipeline
A typical automated compliance flow places a documentation gate at the CI/CD stage, a configuration gate at runtime, and a content or disclosure gate at inference time, with any denial at any gate routed to a human reviewer rather than silently blocked.
Glossary
- Policy as code
- The practice of expressing governance, security, or compliance rules as machine-readable files that a software engine can evaluate automatically.
- Policy engine
- Software, such as Open Policy Agent, that evaluates a request or system state against a defined set of rules and returns an allow or deny decision.
- Rego
- The declarative rule language used by Open Policy Agent to express policy conditions.
- Continuous assurance
- An approach to compliance that checks systems constantly, as part of normal operation, rather than at scheduled audit intervals.
- Inference-time guardrail
- A policy check evaluated at the moment a model serves a live request, capable of blocking or modifying a response before it reaches the user.
- Presence check
- A rule that verifies a required record, field, or timestamp exists, without evaluating the substantive quality of what it contains.
Key Takeaways
- Policy as code turns compliance rules into machine-readable checks that run automatically in CI/CD pipelines, at runtime, or at inference time.
- Open Policy Agent and its Rego language popularized the pattern in cloud infrastructure before it spread into AI governance.
- Automated rules are reliable for presence, threshold, and pattern-match questions, but cannot judge the substantive quality of a control.
- Genuinely ambiguous compliance questions still require human review; the policy engine’s job is to make sure that review actually happens.
- Continuous assurance catches violations in minutes to hours instead of waiting for the next scheduled audit cycle.
- Translating regulatory text into executable rules is an ongoing discipline, not a one-time engineering task, because both the rules and the regulations change.
- Starting with a small number of narrow, well-documented rules produces far fewer false positives than trying to encode an entire regulatory framework at once.
FAQs
What is policy as code in the context of AI governance?
Policy as code means writing compliance and governance rules as machine-readable files that a policy engine evaluates automatically, instead of relying only on manual reviews. In AI governance, this typically checks things like whether required documentation exists, whether a model version is approved, or whether an output violates a defined rule, all without waiting for a scheduled audit.
Can policy as code fully replace human compliance reviewers?
No. Policy as code is reliable for checking presence, thresholds, and patterns, such as confirming a required record exists. It cannot evaluate genuinely ambiguous cases that require weighing context or judgment, so human reviewers remain necessary for those decisions, with the automated system mainly ensuring that review actually happens.
What is Open Policy Agent and why is it relevant here?
Open Policy Agent is an open-source policy engine, created by Tim Hinrichs, Torin Sandall, and Teemu Koponen, that graduated from the Cloud Native Computing Foundation in February 2021. It popularized expressing rules in a declarative language called Rego and has become a common building block for automated compliance systems, including those applied to AI governance.
Where in an AI system should compliance checks run?
Most programs place checks at three points: CI/CD pipeline gates before a model ships, runtime monitoring for configuration drift, and inference-time guardrails on live requests. Each catches different problems, and mature governance programs typically combine more than one enforcement point rather than relying on a single check.
How is continuous assurance different from a traditional compliance audit?
A traditional audit checks a sample of evidence at a scheduled point in time, often months apart. Continuous assurance evaluates systems constantly as part of normal operation, generating evidence automatically and catching violations within minutes to hours rather than waiting for the next audit cycle.
What is the biggest risk of adopting policy as code for AI compliance?
The biggest risk is false confidence: treating a passing automated check as proof that the full underlying regulatory requirement was met, when the rule may only verify a narrow, specific condition like a record’s existence. Governance teams need separate processes to periodically confirm the substance behind each automated signal.
How do teams translate regulatory text into executable rules?
Teams typically identify the specific, checkable fact a regulation is asking for, write a narrow rule that checks only that fact, and document explicitly what the rule does not cover. Because this translation step can introduce errors, mature programs schedule recurring reviews of the translation itself, separate from reviewing the rule’s technical correctness.
Is policy as code only relevant to large enterprises?
No. Smaller teams deploying even a single AI system in a regulated context, such as a hiring tool or a customer-facing chatbot, can benefit from encoding a handful of narrow, high-value rules rather than adopting a full enterprise platform, since the core discipline scales down as easily as it scales up.
References
- Open Policy Agent, official documentation, openpolicyagent.org
- Institute for Law and AI, “Automated Compliance and the Regulation of AI”
- Forbes Technology Council, “From Compliance To Continuous Assurance: Automating Cloud Governance With Policy-As-Code”
- Platform Engineering, “Policy as Code: The Platform Engineer’s Guide to Automated Governance and Compliance”
- Spacelift, “Top 12 Policy as Code (PaC) Tools in 2026”
- arXiv, “Executable Governance for AI: Translating Policies into Rules Using LLMs”
- arXiv, “ArGen: Auto-Regulation of Generative AI via GRPO and Policy-as-Code”
- hoop.dev, “AI Governance Made Simple with Open Policy Agent”
For related coverage on this site, see our deep dive on building guardrails for agentic AI autonomy, which looks at the broader guardrail design question this piece narrows in on. Teams building a formal review structure may also want our guide to building an AI governance committee, our comparison of AI risk management frameworks, our walkthrough of EU AI Act compliance requirements, our explainer on model cards and system cards. Readers evaluating how automated compliance intersects with hiring tools specifically should also read our companion piece on AI and employment law.