| Myth | Reality |
|---|---|
| Liveness detection and deepfake detection are the same technology. | Liveness detection confirms a real, present human is in front of the sensor; deepfake detection analyzes whether captured media has been synthetically generated or manipulated. Modern systems need both, especially now that attackers inject fabricated video instead of holding up a printed photo. |
| A single face-matching selfie check is enough to stop biometric fraud. | A face match alone cannot tell a live person from a high-quality photo, mask, or video replay. Liveness signals such as depth, movement, and challenge-response are required alongside the match. |
| Presentation attacks are the main threat to biometric systems today. | Through 2026 the center of gravity has shifted toward injection attacks, where a fabricated video feed is inserted directly into the software pipeline rather than shown physically to a camera. |
| 3D depth sensing alone makes a system spoof-proof. | Depth sensing raises the bar significantly but is most effective when combined with texture analysis, behavioral signals, and device-level integrity checks, since no single signal is unbeatable in isolation. |
Why Liveness Detection Has Become Essential
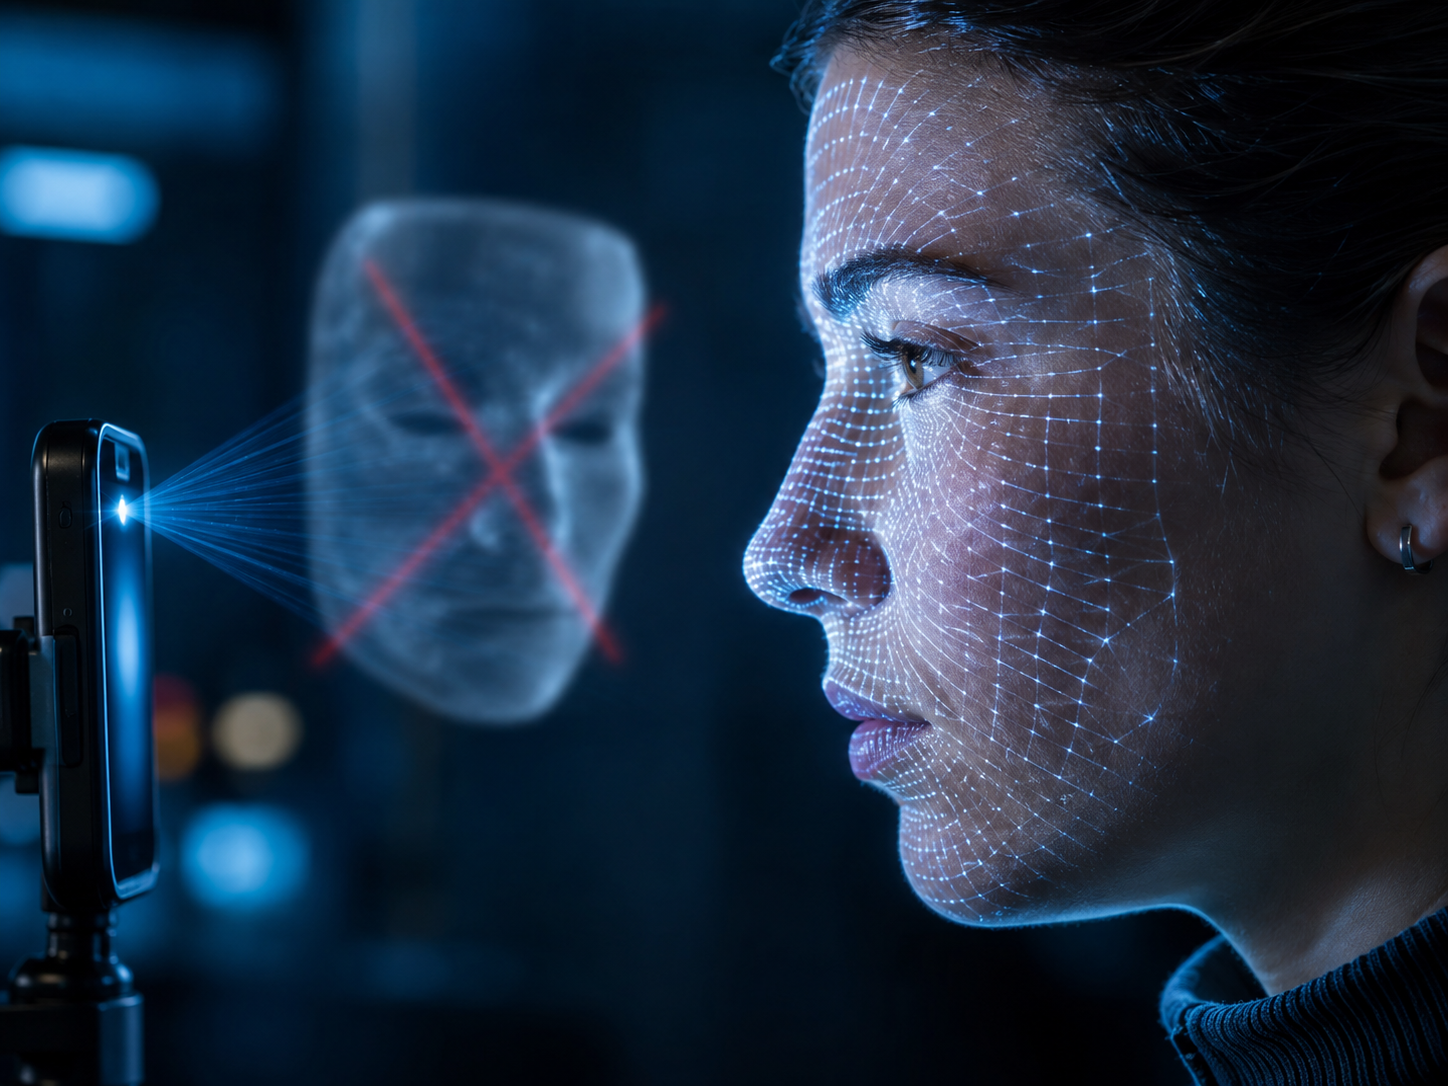
Biometric authentication, whether a face scan to unlock a phone, a fingerprint to approve a payment, or a selfie submitted during identity verification, relies on a simple assumption: the biometric sample being captured belongs to a real, present, consenting person. Liveness detection is the set of techniques designed to test that assumption, distinguishing a genuine live capture from a presentation attack, such as a printed photo, a video played on a screen, or a realistic silicone mask, and increasingly from injection attacks that skip the physical spoof entirely and feed a fabricated stream directly into the camera or microphone input of the verification software.
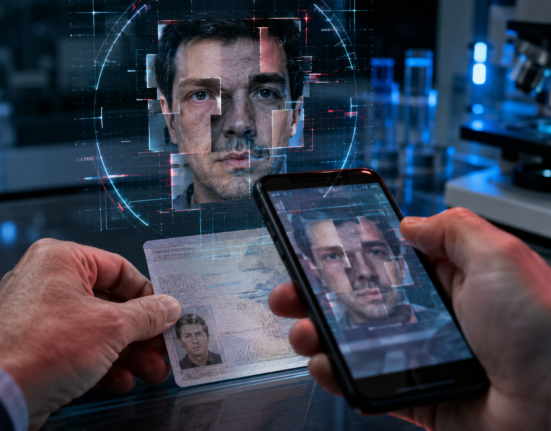
The distinction between liveness detection and deepfake detection matters more than it might seem. Liveness detection asks whether a real human is physically present at the sensor right now. Deepfake and manipulation detection asks whether the media being analyzed, live or recorded, has been synthetically altered or generated. A sophisticated attack can pass a naive liveness check by injecting a synthetic video feed that mimics natural blinking and micro-movements, which is why current best practice treats these as complementary, not interchangeable, layers of defense.
Core Liveness Detection Techniques
Passive Liveness: Texture and Reflectance Analysis
Passive liveness detection analyzes a single image or short clip without requiring the user to perform any action. It examines subtle cues such as skin texture, light reflectance patterns, and micro-color variations caused by blood flow beneath real skin, all of which are difficult for a printed photo, screen replay, or mask to reproduce convincingly. Passive checks are fast and low-friction, making them well suited to everyday unlock scenarios, though they are generally considered a weaker standalone defense than active methods for high-assurance use cases.
Active Liveness: Challenge-Response
Active liveness detection prompts the user to perform a specific action, such as turning their head, blinking on command, or reading a randomly generated number aloud. Because the challenge is unpredictable and generated at the moment of verification, a pre-recorded video or static photo cannot satisfy it. This approach adds user friction but significantly raises the difficulty for an attacker who does not have a live, cooperative feed to work with.
3D Depth Sensing
Depth-sensing cameras, using structured light or time-of-flight sensors, capture a three-dimensional map of a face rather than a flat two-dimensional image. A printed photo or a flat screen replay has no depth structure to detect, and even many silicone masks fail to replicate the precise depth contours of a real face convincingly. Depth sensing is one of the strongest single signals available on modern smartphones equipped with the necessary hardware, though it is not universal across all devices.
Physiological Signal Analysis
Emerging techniques analyze subtle physiological signals invisible to the naked eye, such as remote photoplethysmography, which detects tiny color changes in facial skin caused by blood pulsing with each heartbeat. A photo, mask, or most current deepfake generations do not reproduce this signal naturally, making it a promising additional layer, particularly as a countermeasure to increasingly convincing synthetic video.
Injection Attack Detection
Rather than fooling a camera physically, a growing share of attacks bypass the camera entirely, using virtual camera drivers or manipulated software layers to feed a fabricated video stream directly into the verification application. Defending against this requires device and software integrity checks, verifying that the camera feed genuinely originates from the expected hardware sensor and has not been intercepted or substituted by an unauthorized driver or emulator.
| Attack type | Method | Primary countermeasure |
|---|---|---|
| Printed photo attack | Holding a printed photograph up to the camera | Passive texture analysis, 3D depth sensing |
| Video replay attack | Playing a recorded video of the victim on a screen | Active challenge-response, depth sensing, screen-reflection detection |
| Silicone or latex mask attack | Wearing a realistic physical mask matching the victim’s face | Physiological signal analysis, thermal and depth sensing |
| Deepfake injection attack | Feeding a synthetically generated video stream directly into the software pipeline | Device integrity checks, camera feed authentication, multi-modal fusion |
Multi-Modal Liveness: Combining Signals
No single liveness signal is unbeatable against a sufficiently resourced attacker, which is why leading identity platforms fuse multiple modalities together. A robust verification event might combine facial depth mapping, passive texture analysis, an active challenge-response prompt, voice biometric checks, and behavioral signals such as how naturally a person moves their device during capture, weighting each signal and requiring a combined confidence score above a defined threshold before granting access.
This layered approach mirrors the broader identity security principle of defense in depth: an attacker capable of defeating one signal, such as producing a convincing deepfake video, faces a substantially harder problem when the system also demands proof of device integrity, natural physiological signals, and behavioral plausibility simultaneously.
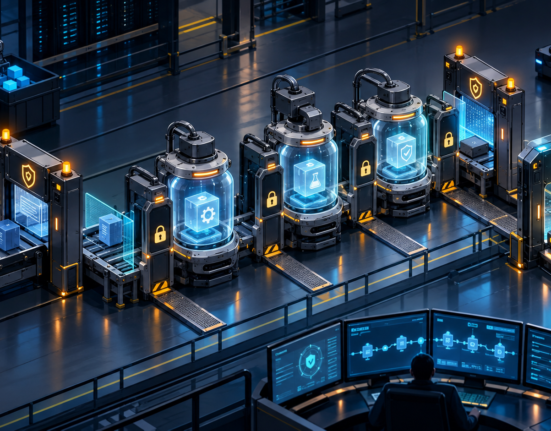
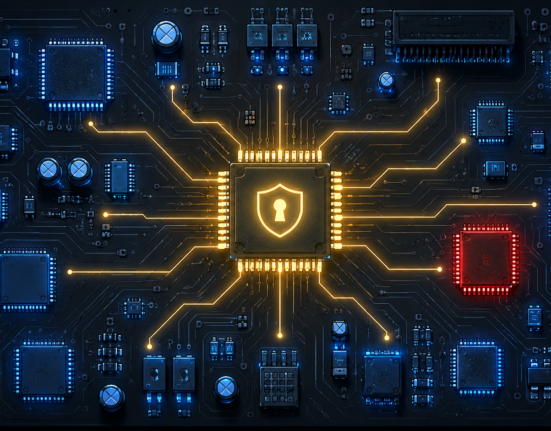
Figure: Three layers of modern biometric spoof defense
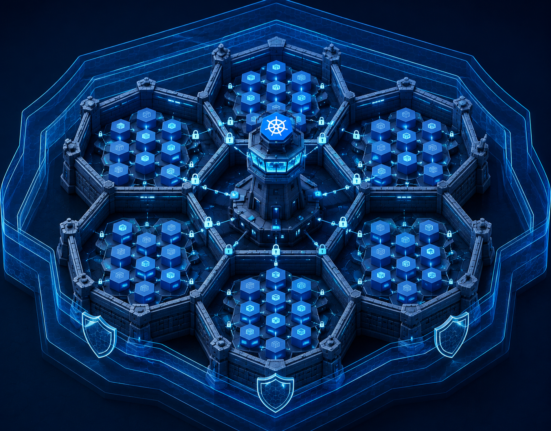
Layer one, presentation attack detection, spots physically presented fakes such as printed photos or masks using texture, depth, and challenge-response analysis. Layer two, injection attack protection, verifies the camera feed itself has not been substituted by a virtual driver or manipulated software layer. Layer three, combined device and biometric verification, requires both a trusted device and a passing biometric match before granting access, closing gaps that either check alone would miss.
| Liveness method | User friction | Hardware requirement | Best suited for |
|---|---|---|---|
| Passive texture analysis | Very low | Standard camera | Everyday device unlock |
| Active challenge-response | Moderate | Standard camera and microphone | Identity verification onboarding |
| 3D depth sensing | Low | Structured light or time-of-flight sensor | High-assurance mobile unlock |
| Physiological signal analysis | Low | Standard camera, higher processing | High-value transaction approval |
| Injection attack detection | None (background check) | Software and device attestation | Remote identity verification and onboarding |
Benchmarking Spoof Resistance
Independent testing programs evaluate presentation attack detection performance using standardized attack types, ranging from simple printed photos to professionally produced silicone masks and high-end video replays. Two figures matter most in these evaluations: the attack presentation classification error rate, measuring how often a genuine spoof is incorrectly accepted as live, and the bona fide presentation classification error rate, measuring how often a real legitimate user is incorrectly rejected. Vendors and enterprises adopting biometric systems should request current results from recognized testing bodies rather than relying on marketing claims, since spoof-resistance performance varies significantly across implementations and attack sophistication levels.
Common Mistake
Common mistake
Treating liveness detection and deepfake detection as interchangeable, or assuming that passing a liveness check guarantees the media has not been manipulated. A system can confirm a live person is physically present while still being fed a manipulated audio or video stream through a compromised software path, which is why injection-attack and device-integrity checks must be evaluated separately from classic presentation attack detection.
What Worked
What worked
Organizations that reduced biometric fraud most effectively adopted multi-modal liveness, fusing facial depth data, passive texture signals, active challenges, and device integrity verification rather than relying on any single method. They also budgeted for regular re-testing against updated attack samples, since spoof techniques, especially AI-generated deepfakes, improve quickly enough that a defense validated a year ago may no longer hold up against current attack quality.
Frequently Overlooked Details
- Presentation attack detection (PAD)The subset of liveness detection focused on physically presented spoofs, such as printed photos, screen replays, or masks shown to a camera.
- Injection attackAn attack that bypasses the physical camera entirely, feeding a fabricated video or audio stream directly into the software verification pipeline.
- Remote photoplethysmography (rPPG)A technique detecting subtle facial color changes caused by blood flow, used as a physiological liveness signal that is difficult for spoofs to replicate.
- Attack presentation classification error rateA standardized metric measuring how often a spoof attack is incorrectly classified as a genuine live presentation.
- Device attestationA cryptographic check confirming that a camera feed or biometric sensor reading genuinely originates from trusted, unmodified hardware.
- Multi-modal fusionCombining several independent liveness and biometric signals into a single confidence score, making it substantially harder for an attacker to defeat every layer simultaneously.
Glossary
- Liveness detection
- A biometric security measure determining whether a captured sample comes from a physically present, live person rather than a spoof artifact or fabricated feed.
- Presentation attack
- An attempt to deceive a biometric system using a fake physical sample, such as a printed photo, video replay, or mask, presented to the sensor.
- Injection attack
- An attack technique that inserts a fabricated data stream directly into a device or software pipeline, bypassing the need to physically present a spoof to a sensor.
- Deepfake
- Synthetic media, typically video or audio, generated or manipulated by artificial intelligence to convincingly imitate a real person’s appearance or voice.
- 3D depth sensing
- A hardware capability that captures three-dimensional facial structure using structured light or time-of-flight technology, distinguishing real faces from flat images.
Key Takeaways
- Liveness detection confirms a real person is present; deepfake detection confirms media has not been synthetically manipulated, and modern systems need both.
- Passive texture analysis, active challenge-response, 3D depth sensing, and physiological signal analysis each catch different categories of spoof attacks.
- Attacker focus has shifted from physical presentation attacks toward injection attacks that feed fabricated video directly into software pipelines.
- No single liveness signal is unbeatable; multi-modal fusion combining several independent signals produces the strongest spoof resistance.
- Device and software integrity checks are necessary to catch injection attacks that a purely camera-based liveness check would miss.
- Independent testing using standardized attack presentation and bona fide error rates should guide vendor selection, not marketing claims alone.
- Spoof detection defenses need regular re-validation, since AI-generated deepfake quality continues to improve rapidly.
FAQs
What is the difference between liveness detection and deepfake detection?
Liveness detection verifies that a real, physically present person is providing the biometric sample at capture time. Deepfake detection analyzes whether the media itself, live or recorded, has been synthetically generated or manipulated. Modern systems increasingly need both, since an injection attack can present a synthetic feed that still passes basic liveness signals.
Can a printed photo still fool a modern biometric system?
A well-designed system combining 3D depth sensing, texture analysis, and challenge-response would typically catch a simple printed photo, since flat images lack the depth structure and micro-movement cues that real faces produce. Weaker systems relying only on basic face matching remain vulnerable to this attack type.
What is an injection attack in biometric security?
An injection attack bypasses the physical camera or microphone entirely, using a virtual driver or manipulated software layer to feed a fabricated video or audio stream directly into the verification application, rather than presenting a physical spoof for the sensor to capture.
How does 3D depth sensing improve spoof resistance?
Depth sensing captures the three-dimensional structure of a face using structured light or time-of-flight hardware, which a flat printed photo or screen replay cannot reproduce, and which even many physical masks fail to replicate with sufficient precision, making it one of the stronger individual liveness signals available.
Why do security teams combine multiple liveness detection methods?
No individual signal, whether depth sensing, texture analysis, or challenge-response, is unbeatable against a sufficiently resourced attacker. Combining several independent methods into a multi-modal fusion score makes it substantially harder for an attacker to simultaneously defeat every layer of defense.
What metrics are used to benchmark biometric spoof resistance?
Independent testing programs commonly report the attack presentation classification error rate, measuring how often spoof attacks are incorrectly accepted, alongside the bona fide presentation classification error rate, measuring how often genuine users are incorrectly rejected, giving a balanced view of both security and usability performance.
Are voice biometrics vulnerable to deepfake attacks too?
Yes, voice cloning technology has advanced significantly, and voice biometric systems face similar liveness and injection attack challenges as facial biometrics. Effective voice authentication increasingly pairs voice matching with challenge-response phrases and audio integrity checks to detect synthetic or replayed audio.
Does liveness detection add significant friction for legitimate users?
It depends on the method. Passive techniques like texture and depth analysis run in the background with minimal added friction, while active challenge-response methods require an explicit user action. Well-designed systems balance these methods by risk level, reserving higher-friction active checks for higher-value transactions.
References
- Keyless, “Deepfakes and Authentication in 2026: Hype vs. Reality”
- Biometric Update, “Injection Attack Detection Critical to Digital Security Yet Often Misunderstood”
- OLOID, “Liveness Detection Guide: Protecting Digital Identity 2026”
- Recognito, “Presentation Attack Detection for Stronger Biometric Security”
- DeepIDV, “Multi-Modal Liveness: The New Standard for Biometric Assurance”
- DeepIDV, “Biometric Verification in 2026: What Has Changed and What Is Next”
For related reading, see how protecting digital identity from deepfakes covers the broader synthetic media threat landscape, why hardware-backed sensors matter in our guide to device identity and hardware-rooted trust, how liveness checks reinforce passwordless authentication with passkeys and FIDO2, why behavioral signals extend protection after login in continuous authentication using behavioural signals, and how biometric liveness supports identity proofing against fabricated identities in identity verification against synthetic identities.